An AI security platform that runs autonomous agents across code, cloud, and CI/CD to find vulnerabilities, test whether they're actually exploitable, and ship the fix — instead of adding another alert to a queue no one clears.
tolmo.com
Mobile apps that handle money or sensitive data are a constant target for reverse engineering and tampering, but the usual fix — integrating an SDK and rebuilding security logic into the app — takes weeks of engineering time most teams don't have to spare. RASPIRE skips that step entirely: it works post-compile, applying AI-tuned defenses directly to the built binary without touching source code or requiring an SDK integration. It protects against a wide range of runtime attacks — reverse engineering, tampering, repackaging, debugging, hooking tools, emulators, MITM and certificate-pinning bypass, rooted/jailbroken device abuse, and screen capture — across native Android and iOS as well as cross-platform frameworks like Flutter, React Native, Ionic, Cordova, Xamarin, and Unity. It also extends to protecting on-device AI models and business logic from extraction, and supports both cloud and on-premises deployment for compliance-sensitive organizations (OWASP MASVS, PCI DSS, GDPR, HIPAA, SOC 2). Founded in 2024 and backed by Y Combinator, RASPIRE doesn't publish pricing — there's no pricing page, and access goes through a sales conversation.
| # | Tool | Best for | Price |
|---|---|---|---|
| 1 | Équipes de sécurité et CTOs responsables des environnements de production cherchant à réduire le délai de résolution des vulnérabilités | — | |
| 2 | Organisations développant ou déployant des agents IA customer-facing ayant besoin de vérifier la robustesse face aux attaques adversariales | — | |
| 3 | Organisations santé, cryptomonnaie et banque/fintech vulnérables aux attaques d'infrastructure web | — | |
| 4 | Développeurs et équipes utilisant Claude Desktop ou Cursor avec des serveurs MCP tiers, soucieux de la sécurité des appels d'outils IA | — | |
| 5 | Site owners and developers managing AI crawler access | — | |
| 6 | Privacy-conscious users wanting model-agnostic AI access from their browser | — | |
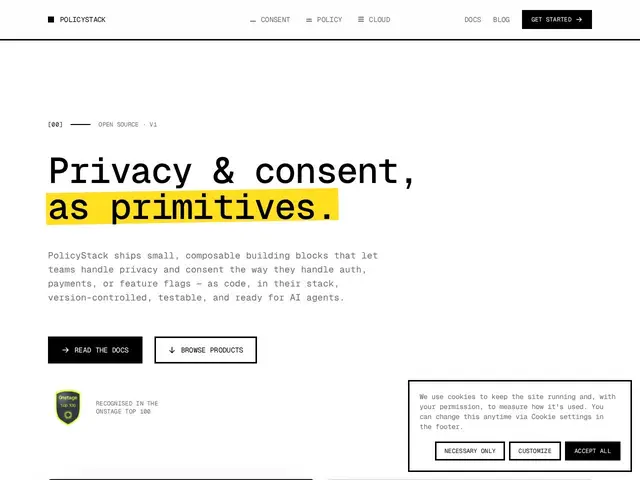
| 7 | Developers wanting privacy/consent management integrated into their codebase | — | |
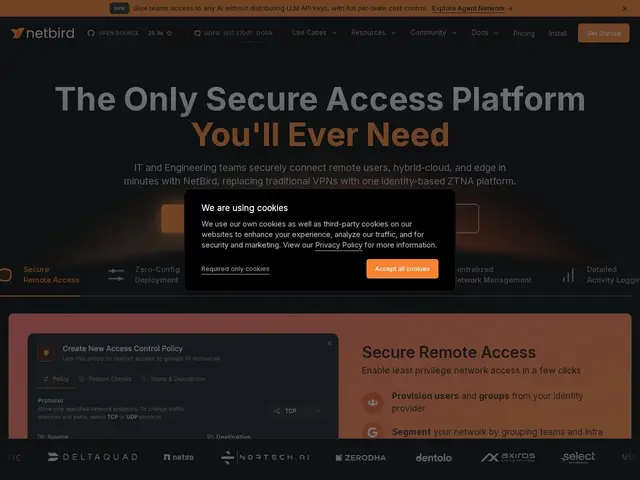
| 8 | IT/DevOps teams replacing corporate VPNs with Zero Trust access | — | |
| 9 | Businesses needing GDPR-compliant, frictionless bot protection | — | |
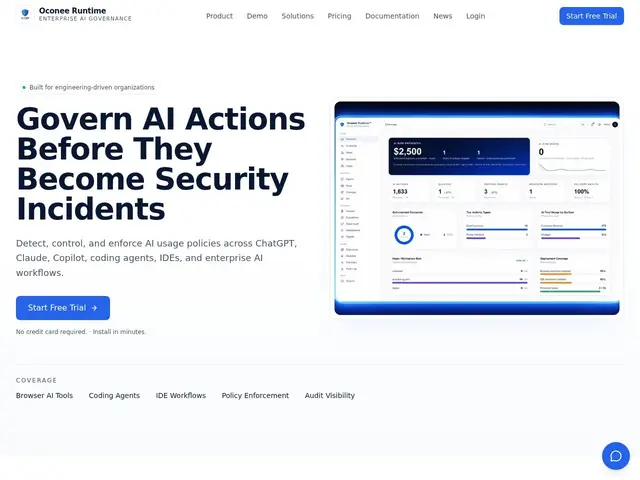
| 10 | Organisations d'ingénierie, équipes sécurité/conformité adoptant des agents de code IA | — | |
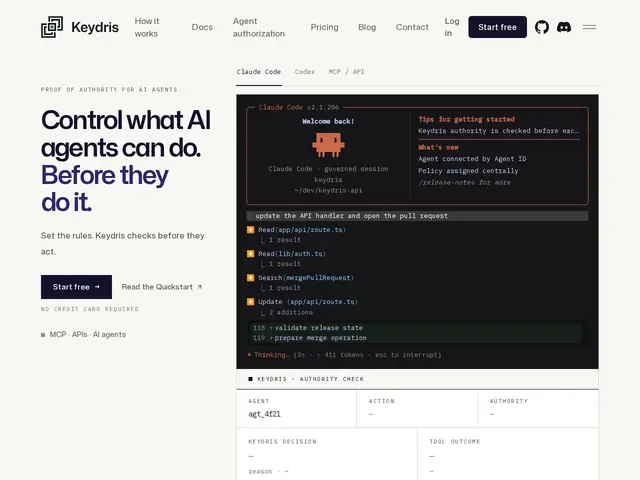
| 11 | Équipes MCP/API et sécurité déployant des agents IA | — | |
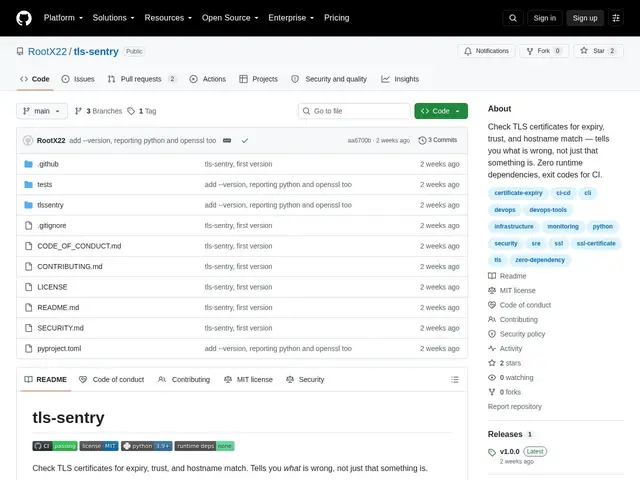
| 12 | Équipes DevOps/SRE et administrateurs système voulant un moniteur d'expiration de certificat sans dépendance pour cron/CI | — |
An AI security platform that runs autonomous agents across code, cloud, and CI/CD to find vulnerabilities, test whether they're actually exploitable, and ship the fix — instead of adding another alert to a queue no one clears.
An adversarial verification platform that runs offensive attack simulations against AI agents to find and block vulnerabilities before real attackers do, with custom pricing on request.
A web infrastructure security platform, founded by the Princeton team behind the internet's Multi-Perspective Issuance Corroboration standard, that detects and defends against impersonation attacks on websites and APIs.
macOS app that intercepts and audits MCP server traffic between Claude Desktop or Cursor and connected tools for security oversight.
Free, in-browser generator for robots.txt and llms.txt files that control which AI crawlers can access your site.
Privacy-first browser side panel AI assistant that works with any model or agent and anonymizes sensitive data before it leaves your browser.
Open-source, developer-first privacy and cookie-consent infrastructure with headless consent flows and version-controlled policies.
Open-source WireGuard-based mesh VPN that replaces traditional VPNs with Zero Trust, identity-based device access.
Invisible, privacy-first bot protection using proof-of-work instead of visual puzzles.
Enterprise policy-enforcement layer that watches what coding agents do — prompts, commands, file changes — and blocks or alerts on sensitive data exposure.
Authorization layer that checks every AI agent action against a policy before it runs, with per-action revocation and a full audit trail.
A free Python command-line tool that checks a website's HTTPS certificate and tells you exactly what's wrong with it — expired, untrusted, wrong hostname — instead of a generic connection error.