A fast, open-source, static analysis tool for finding bugs and enforcing code standards at editor, commit, and CI time. Its rules look like the code you already write; no abstract syntax trees or regex wrestling. Supports 17+ languages.
semgrep.dev
AI coding assistants are great at shipping features fast and notoriously bad at remembering to check who's allowed to see what — the kind of mistake that lets anyone view someone else's data just by changing an ID in the URL. VulX exists specifically to catch the security gaps that "vibe coding" tends to leave behind. VulX reads an entire application's codebase to check for exposed keys, vulnerable dependencies, insecure storage rules, and injection vulnerabilities, with particular focus on authorization flaws — routes that hand over any record to anyone who edits the ID in the URL, a pattern that has affected several high-profile AI-built apps. The free "Watch" tier connects to a GitHub repository and runs recurring scans, including CVE checks twice daily, secret detection, and a three-model consensus approach designed to reduce false positives before a finding reaches human review. Findings come with exact file and line locations and plain-English explanations of how to fix them, and an API is available for wiring automated security checks into CI/CD pipelines; a scoped Enterprise engagement covers deeper, hands-on application review.
| # | Tool | Best for | Price |
|---|---|---|---|
| 1 | Développeurs | — | |
| 2 | Développeurs | — | |
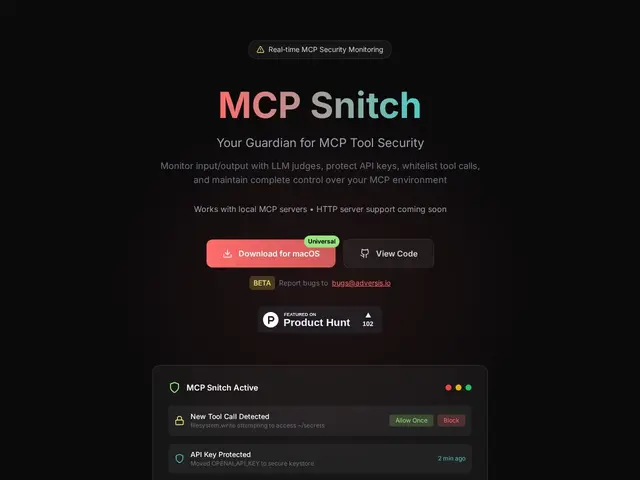
| 3 | Développeurs et équipes utilisant Claude Desktop ou Cursor avec des serveurs MCP tiers, soucieux de la sécurité des appels d'outils IA | — | |
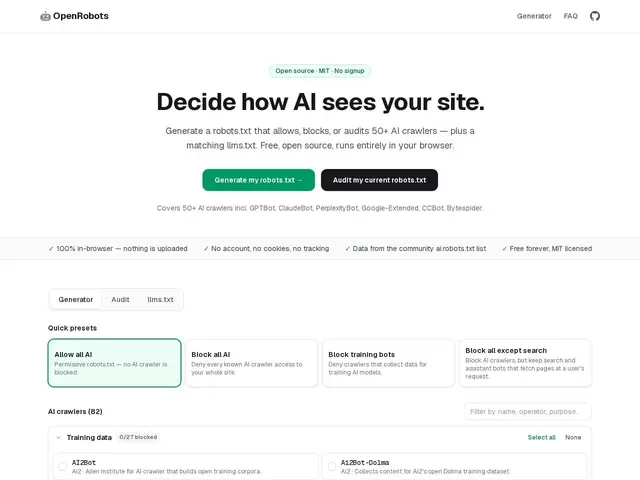
| 4 | Site owners and developers managing AI crawler access | — | |
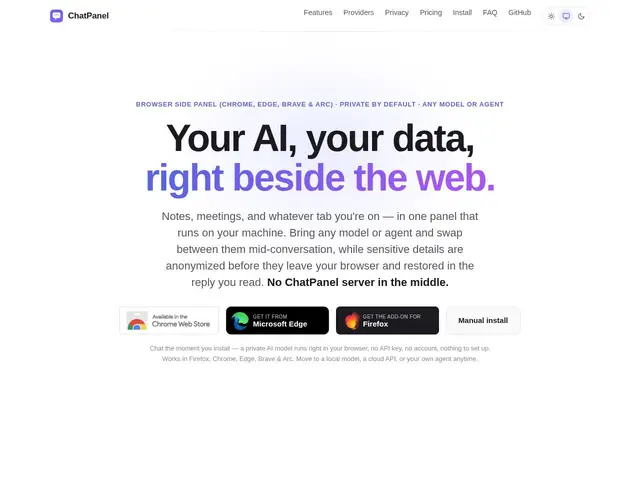
| 5 | Privacy-conscious users wanting model-agnostic AI access from their browser | — | |
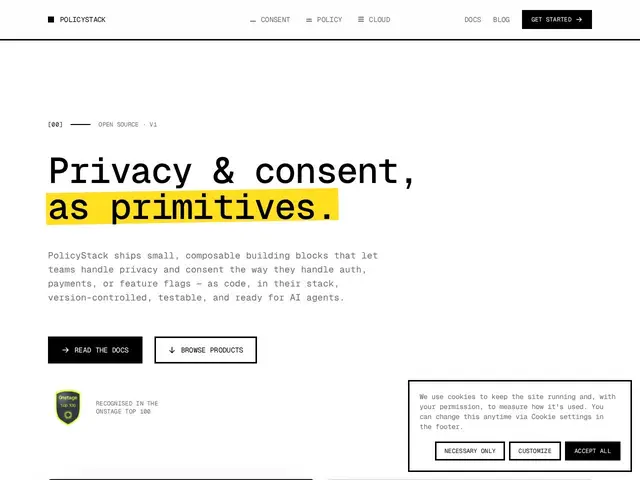
| 6 | Developers wanting privacy/consent management integrated into their codebase | — | |
| 7 | IT/DevOps teams replacing corporate VPNs with Zero Trust access | — | |
| 8 | Businesses needing GDPR-compliant, frictionless bot protection | — | |
| 9 | Organisations d'ingénierie, équipes sécurité/conformité adoptant des agents de code IA | — | |
| 10 | Équipes MCP/API et sécurité déployant des agents IA | — | |
| 11 | Équipes DevOps/SRE et administrateurs système voulant un moniteur d'expiration de certificat sans dépendance pour cron/CI | — | |
| 12 | Équipes construisant des applications LLM soumises à des exigences de conformité (RGPD, AI Act) et de protection des données | — |
macOS app that intercepts and audits MCP server traffic between Claude Desktop or Cursor and connected tools for security oversight.
Free, in-browser generator for robots.txt and llms.txt files that control which AI crawlers can access your site.
Privacy-first browser side panel AI assistant that works with any model or agent and anonymizes sensitive data before it leaves your browser.
Open-source, developer-first privacy and cookie-consent infrastructure with headless consent flows and version-controlled policies.
Open-source WireGuard-based mesh VPN that replaces traditional VPNs with Zero Trust, identity-based device access.
Invisible, privacy-first bot protection using proof-of-work instead of visual puzzles.
Enterprise policy-enforcement layer that watches what coding agents do — prompts, commands, file changes — and blocks or alerts on sensitive data exposure.
Authorization layer that checks every AI agent action against a policy before it runs, with per-action revocation and a full audit trail.
A free Python command-line tool that checks a website's HTTPS certificate and tells you exactly what's wrong with it — expired, untrusted, wrong hostname — instead of a generic connection error.
An open-source trust-boundary gateway that sits in front of OpenAI, Anthropic and Gemini API traffic to redact PII, enforce rate limits, and track usage without touching your app code.