Find web app vulnerabilities, audit for OWASP Risks
qualys.com
Vulnerability scanning tools have a well-known usability problem: the best open-source scanners (OpenVAS, ZAP, Nmap) are genuinely powerful, but running them yourself means managing separate tools, schedules and infrastructure, and their raw output reads like a wall of CVE IDs that's hard to act on without a dedicated security engineer. Panoptic Scans packages those same open-source engines into a managed, scheduled service and translates the findings into readable 'attack narrative' reports, so a smaller team can get continuous scanning without hiring a full security function. The platform combines OpenVAS (network vulnerability assessment), ZAP (web application scanning), Nmap (port/service detection) and Nuclei for automated, scheduled scans covering OWASP Top 10 web app issues and network misconfigurations, with email alerting, white-label reporting for agencies/MSPs, and Vanta integration for teams tracking SOC 2 compliance. Pricing is Basic ($25/month, 75 targets), Premium ($75/month, 300 targets) and Pro ($200/month, 7,500 targets), with a 10% discount on annual billing.
| # | Tool | Best for | Price |
|---|---|---|---|
| 1 | Développeurs | Professionnels de la sécurité | — | |
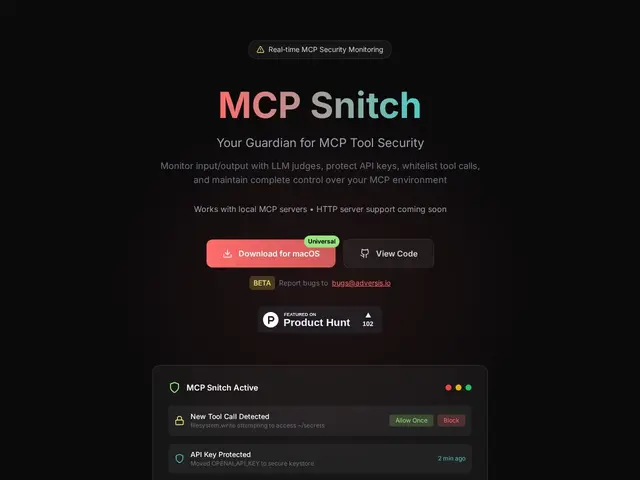
| 2 | Développeurs et équipes utilisant Claude Desktop ou Cursor avec des serveurs MCP tiers, soucieux de la sécurité des appels d'outils IA | — | |
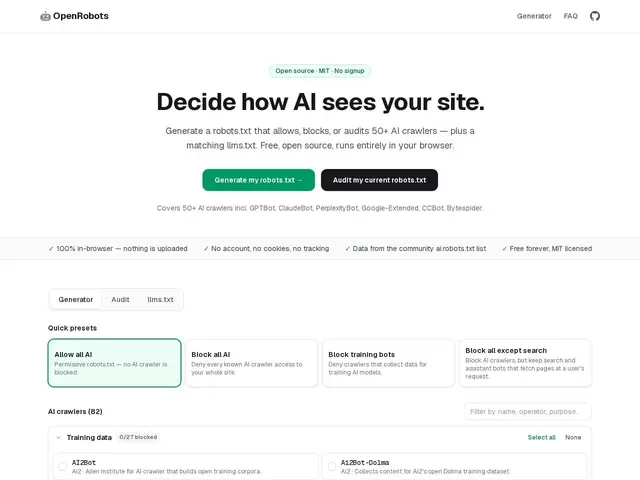
| 3 | Site owners and developers managing AI crawler access | — | |
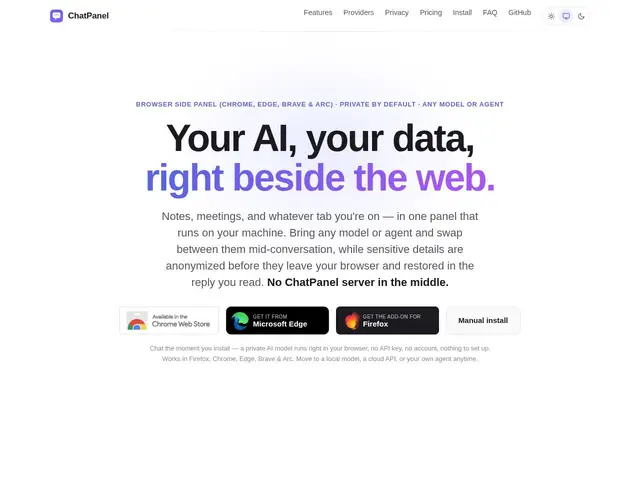
| 4 | Privacy-conscious users wanting model-agnostic AI access from their browser | — | |
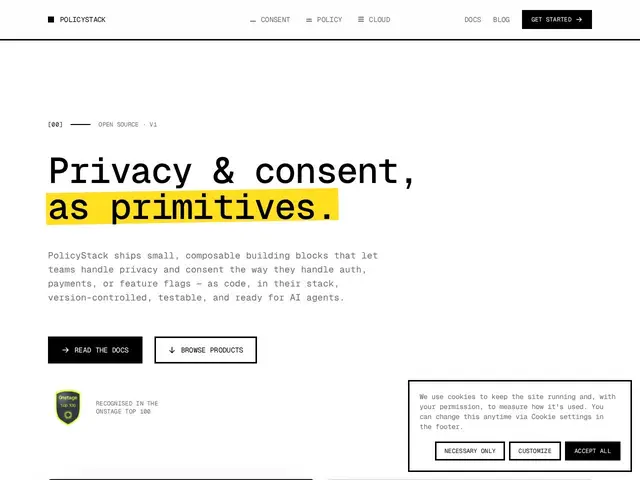
| 5 | Developers wanting privacy/consent management integrated into their codebase | — | |
| 6 | IT/DevOps teams replacing corporate VPNs with Zero Trust access | — | |
| 7 | Businesses needing GDPR-compliant, frictionless bot protection | — | |
| 8 | Organisations d'ingénierie, équipes sécurité/conformité adoptant des agents de code IA | — | |
| 9 | Équipes MCP/API et sécurité déployant des agents IA | — | |
| 10 | Équipes DevOps/SRE et administrateurs système voulant un moniteur d'expiration de certificat sans dépendance pour cron/CI | — | |
| 11 | Équipes construisant des applications LLM soumises à des exigences de conformité (RGPD, AI Act) et de protection des données | — | |
| 12 | Développeurs et petites équipes voulant committer des secrets chiffrés dans Git sans gestionnaire cloud | — |
macOS app that intercepts and audits MCP server traffic between Claude Desktop or Cursor and connected tools for security oversight.
Free, in-browser generator for robots.txt and llms.txt files that control which AI crawlers can access your site.
Privacy-first browser side panel AI assistant that works with any model or agent and anonymizes sensitive data before it leaves your browser.
Open-source, developer-first privacy and cookie-consent infrastructure with headless consent flows and version-controlled policies.
Open-source WireGuard-based mesh VPN that replaces traditional VPNs with Zero Trust, identity-based device access.
Invisible, privacy-first bot protection using proof-of-work instead of visual puzzles.
Enterprise policy-enforcement layer that watches what coding agents do — prompts, commands, file changes — and blocks or alerts on sensitive data exposure.
Authorization layer that checks every AI agent action against a policy before it runs, with per-action revocation and a full audit trail.
A free Python command-line tool that checks a website's HTTPS certificate and tells you exactly what's wrong with it — expired, untrusted, wrong hostname — instead of a generic connection error.
An open-source trust-boundary gateway that sits in front of OpenAI, Anthropic and Gemini API traffic to redact PII, enforce rate limits, and track usage without touching your app code.
A free command-line tool that encrypts your .env secrets file so you can safely commit it to Git, with a pre-commit hook that catches accidental leaks before they happen.