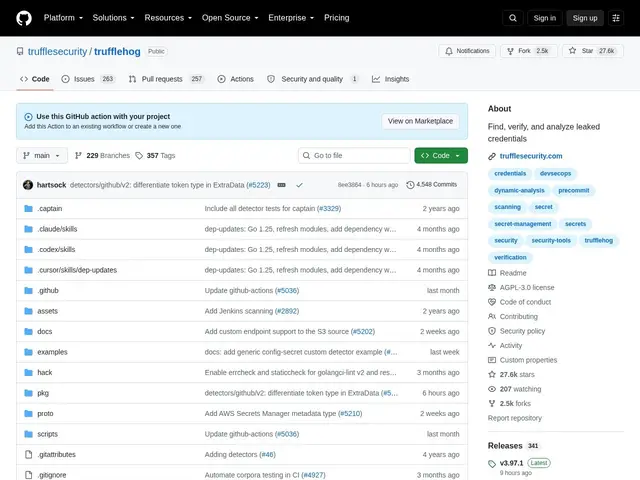
A credential-scanning tool that searches Git repos, cloud storage and other sources for leaked secrets, then actively verifies each one against the real service so you know instantly which leaks are live.
github.com
AI coding assistants like Cursor or Claude Code work by reading through a codebase — which is exactly the problem, because that codebase might also contain a `.env` file full of API keys, a test fixture with real customer data, or internal notes nobody meant to hand to a third-party model. Most people rely on remembering to keep that stuff out of the way, which fails eventually. Offsend automates the memory: like a `.gitignore` file, but for what an AI agent is allowed to read. Offsend is an open-source, local-first boundary layer for AI coding agents. A single `.offsend.yml` config file defines which paths and patterns are off-limits, and runtime gates enforce that boundary for supported tools (Cursor, Codex, Windsurf, Claude Code). It scans content for API keys, tokens, and other sensitive patterns entirely on-device — nothing is uploaded to a cloud service to do the check. The project also ships a CLI, git-hook integration to catch secrets before a commit, and a browser extension that masks sensitive text (keys, emails, phone numbers) before it's pasted into a web-based AI chat. The homepage is explicit that this is a research project, not yet production-ready — worth knowing before building a security policy around it.
| # | Tool | Best for | Price |
|---|---|---|---|
| 1 | Équipes DevSecOps et ingénieurs sécurité voulant détecter et vérifier des secrets exposés | — | |
| 2 | Équipes de développement et DevSecOps voulant empêcher les fuites de secrets dans git | — | |
| 3 | Développeurs | — | |
| 4 | Développeurs et équipes utilisant Claude Desktop ou Cursor avec des serveurs MCP tiers, soucieux de la sécurité des appels d'outils IA | — | |
| 5 | Site owners and developers managing AI crawler access | — | |
| 6 | Privacy-conscious users wanting model-agnostic AI access from their browser | — | |
| 7 | Developers wanting privacy/consent management integrated into their codebase | — | |
| 8 | IT/DevOps teams replacing corporate VPNs with Zero Trust access | — | |
| 9 | Businesses needing GDPR-compliant, frictionless bot protection | — | |
| 10 | Organisations d'ingénierie, équipes sécurité/conformité adoptant des agents de code IA | — | |
| 11 | Équipes MCP/API et sécurité déployant des agents IA | — | |
| 12 | Équipes DevOps/SRE et administrateurs système voulant un moniteur d'expiration de certificat sans dépendance pour cron/CI | — |
A credential-scanning tool that searches Git repos, cloud storage and other sources for leaked secrets, then actively verifies each one against the real service so you know instantly which leaks are live.
A fast, open-source scanner that detects hardcoded secrets — passwords, API keys, tokens — in git history, files or CI pipelines using customizable regex rules.
macOS app that intercepts and audits MCP server traffic between Claude Desktop or Cursor and connected tools for security oversight.
Free, in-browser generator for robots.txt and llms.txt files that control which AI crawlers can access your site.
Privacy-first browser side panel AI assistant that works with any model or agent and anonymizes sensitive data before it leaves your browser.
Open-source, developer-first privacy and cookie-consent infrastructure with headless consent flows and version-controlled policies.
Open-source WireGuard-based mesh VPN that replaces traditional VPNs with Zero Trust, identity-based device access.
Invisible, privacy-first bot protection using proof-of-work instead of visual puzzles.
Enterprise policy-enforcement layer that watches what coding agents do — prompts, commands, file changes — and blocks or alerts on sensitive data exposure.
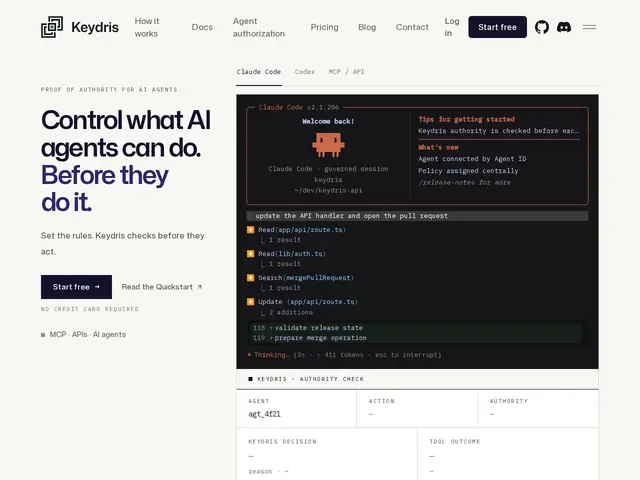
Authorization layer that checks every AI agent action against a policy before it runs, with per-action revocation and a full audit trail.
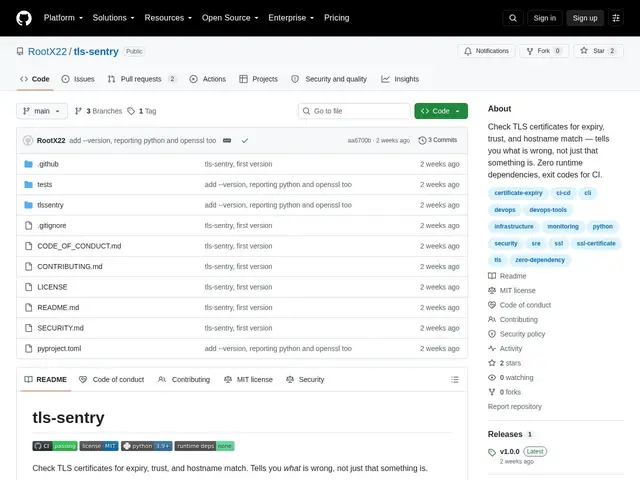
A free Python command-line tool that checks a website's HTTPS certificate and tells you exactly what's wrong with it — expired, untrusted, wrong hostname — instead of a generic connection error.