A security team running five different scanners (one for containers, one for code, one for dependencies...) ends up with five different spreadsheets of findings, half of them duplicates. DefectDojo pulls all of that into one place, removes the duplicates,
Best alternatives to VulnScout in 2026
Modern software is built from hundreds of open-source packages, and any one of them can quietly carry a known vulnerability. Regulations and big customers increasingly ask for an SBOM — a software bill of materials, basically an ingredients list — but having the list isn't the same as knowing which ingredients are actually dangerous right now. VulnScout reads that ingredients list and cross-checks it against vulnerability databases automatically, the way a nutrition app scans a barcode and tells you about allergens instead of making you read the label yourself. VulnScout is an open-source (GPL-3.0) tool from Savoir-faire Linux that ingests SBOMs in multiple formats (SPDX 2/3, CycloneDX, Yocto CVE, OpenVEX) and enriches them with vulnerability data from the NVD, EPSS, and Grype. It provides a web-based triage interface, project/variant management for tracking multiple software builds, CI/CD integration with configurable pass/fail conditions, and report generation in AsciiDoc, HTML, PDF, or CSV — useful for both internal review and compliance documentation. It deploys via Docker and supports organization-specific CVSS scoring adjustments.
Quick comparison of VulnScout alternatives
| # | Tool | Best for | Price |
|---|---|---|---|
| 1 | Équipes AppSec/sécurité qui font tourner plusieurs scanners (SAST, DAST, conteneurs, dépendances...) et veulent centraliser les résultats | — | |
| 2 | Développeurs | — | |
| 3 | Développeurs | — | |
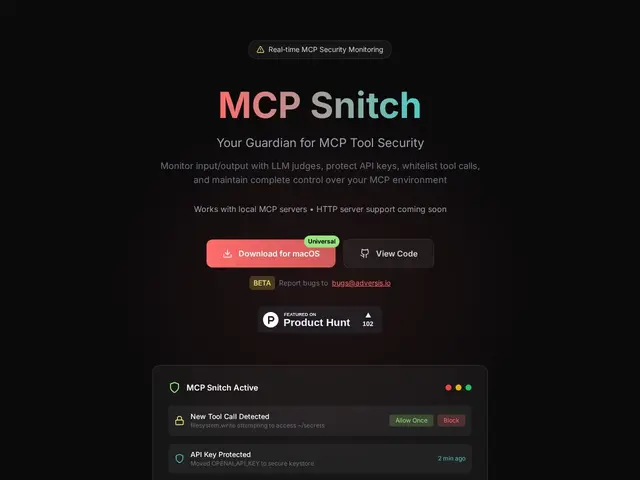
| 4 | Développeurs et équipes utilisant Claude Desktop ou Cursor avec des serveurs MCP tiers, soucieux de la sécurité des appels d'outils IA | — | |
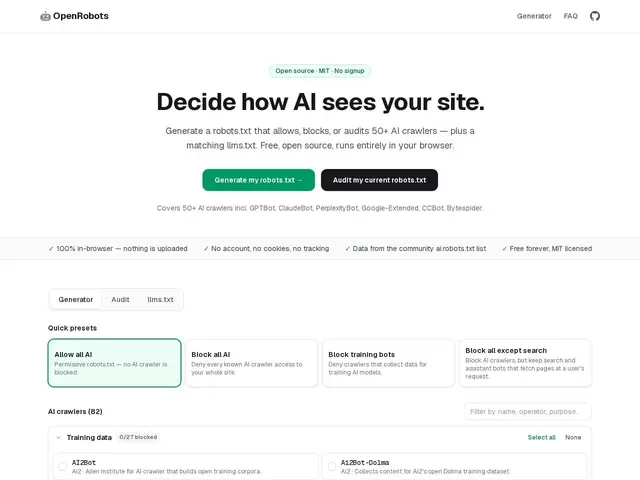
| 5 | Site owners and developers managing AI crawler access | — | |
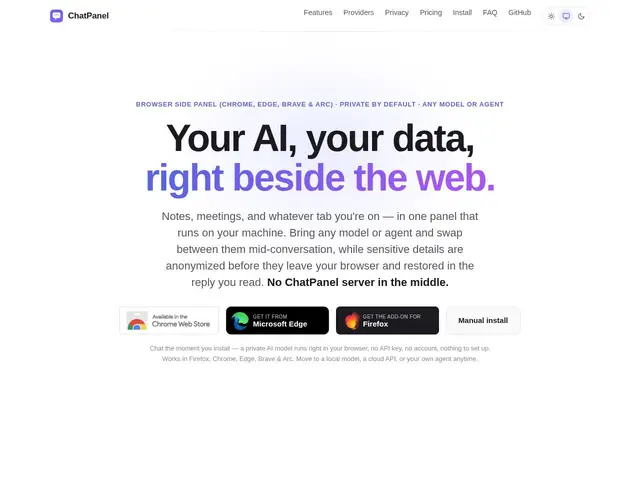
| 6 | Privacy-conscious users wanting model-agnostic AI access from their browser | — | |
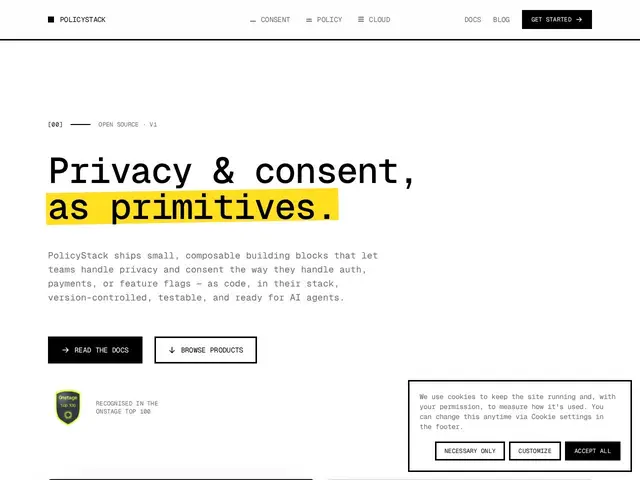
| 7 | Developers wanting privacy/consent management integrated into their codebase | — | |
| 8 | IT/DevOps teams replacing corporate VPNs with Zero Trust access | — | |
| 9 | Businesses needing GDPR-compliant, frictionless bot protection | — | |
| 10 | Organisations d'ingénierie, équipes sécurité/conformité adoptant des agents de code IA | — | |
| 11 | Équipes MCP/API et sécurité déployant des agents IA | — | |
| 12 | Équipes DevOps/SRE et administrateurs système voulant un moniteur d'expiration de certificat sans dépendance pour cron/CI | — |
- ✓ Mature, widely adopted (4,900+ GitHub stars, 38M+ downloads)
- ✓ Aggregates and deduplicates findings from 500+ security tools
macOS app that intercepts and audits MCP server traffic between Claude Desktop or Cursor and connected tools for security oversight.
- ✓ Purpose-built for MCP, not a repurposed generic tool
- ✓ Free, open-source option under GPL-3.0
Free, in-browser generator for robots.txt and llms.txt files that control which AI crawlers can access your site.
- ✓ 100% client-side — no account, no data leaves your browser
- ✓ Covers 82+ named AI crawlers with sensible presets
Privacy-first browser side panel AI assistant that works with any model or agent and anonymizes sensitive data before it leaves your browser.
- ✓ Works with any AI model or agent — in-browser, local, cloud API, or coding agents like Claude Code/Copilot
- ✓ Anonymizes sensitive data (emails, phone numbers, card numbers) before it leaves your browser, restores it in the reply
Open-source, developer-first privacy and cookie-consent infrastructure with headless consent flows and version-controlled policies.
- ✓ Fully open-source (Apache-2.0) with a public commitment to never relicense or paywall features
- ✓ Lightweight headless consent engine (under 4kb core)
Open-source WireGuard-based mesh VPN that replaces traditional VPNs with Zero Trust, identity-based device access.
- ✓ Open-source (BSD-3-Clause + AGPLv3) with 28.9k GitHub stars and active development
- ✓ WireGuard-based peer-to-peer mesh is faster and simpler than routing through a central VPN gateway
Invisible, privacy-first bot protection using proof-of-work instead of visual puzzles.
- ✓ Invisible — no puzzles, no user friction
- ✓ GDPR-compliant by design, zero personal data collected
Enterprise policy-enforcement layer that watches what coding agents do — prompts, commands, file changes — and blocks or alerts on sensitive data exposure.
- ✓ Visibilité temps réel sur les actions des agents IA
- ✓ Détection/blocage de données sensibles et credentials
Authorization layer that checks every AI agent action against a policy before it runs, with per-action revocation and a full audit trail.
- ✓ Vérification par action, pas seulement par clé API
- ✓ Révocation ciblée sans tuer tout le processus
A free Python command-line tool that checks a website's HTTPS certificate and tells you exactly what's wrong with it — expired, untrusted, wrong hostname — instead of a generic connection error.
- ✓ Zero dependencies, easy to drop into bare servers or containers
- ✓ Detailed diagnostics rather than a generic 'connection failed'
FAQ about VulnScout alternatives
- What is the best alternative to VulnScout in 2026?
- Based on our selection, DefectDojo is the best alternative to VulnScout in 2026. A security team running five different scanners (one for containers, one for code, one for dependencies...) ends up with five different spreadsheets of findings, half of them duplicates. DefectDojo pulls all of that into one place, removes the duplicates,. See our full ranking above to compare all options.
- Is VulnScout free?
- VulnScout is a paid tool. Several alternatives in our selection offer free or freemium versions.
- How many alternatives to VulnScout are there?
- mySelectas has listed 12 alternatives to VulnScout in the Security & Privacy category. Our selection is updated regularly to include the best options available.