GitHub repository: grype by anchore
github.com
Knowing whether the container images actually running in your Kubernetes cluster right now have known vulnerabilities usually means either installing a cluster-side agent or scanning images at build time and hoping nothing drifted since. StackRadar CLI takes a simpler approach: run it from your own machine, and it scans every running pod's images directly, no agent, no account, no cluster changes required. It deduplicates images by digest before scanning (so you're not re-checking the same image 50 times across pods), matches installed packages against the OSV (Open Source Vulnerabilities) database, and specifically flags anything listed in CISA's Known Exploited Vulnerabilities catalog — the subset of CVEs actually being exploited in the wild, which matters more for prioritization than a raw CVE count. It's a single static Go binary built on the osv-scanner library, works with your existing registry credentials, and outputs to table, JSON, or an interactive HTML report. CLI flags cover scanning the current cluster, a single image, serving an interactive report, or gating CI with a `--fail-on` severity threshold. It's Apache-2.0 licensed and free, though still early — 5 commits and 3 stars at time of review.
| # | Tool | Best for | Price |
|---|---|---|---|
| 1 | Développeurs | — | |
| 2 | Développeurs | — | |
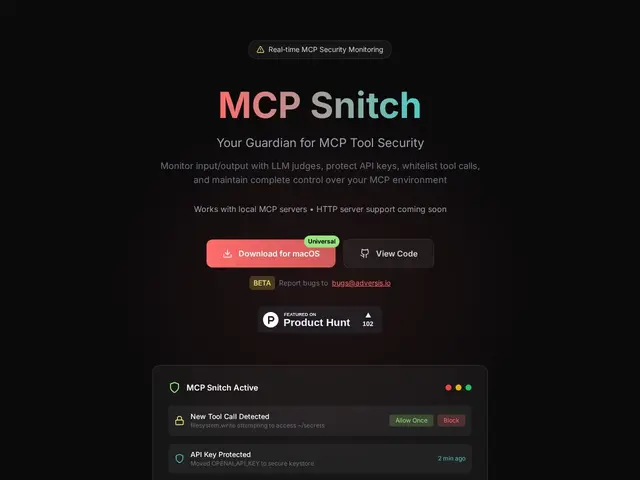
| 3 | Développeurs et équipes utilisant Claude Desktop ou Cursor avec des serveurs MCP tiers, soucieux de la sécurité des appels d'outils IA | — | |
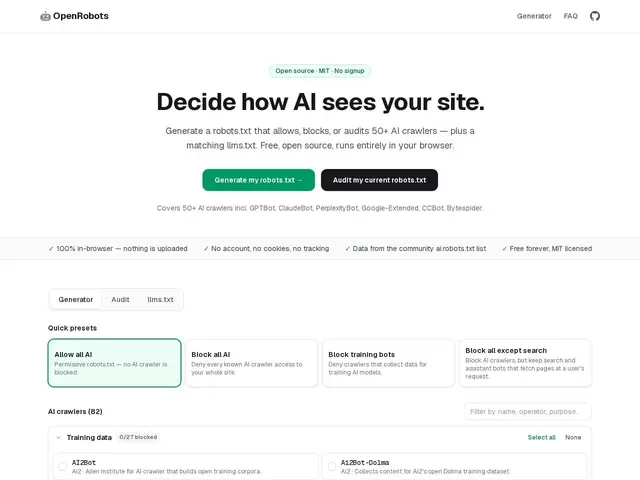
| 4 | Site owners and developers managing AI crawler access | — | |
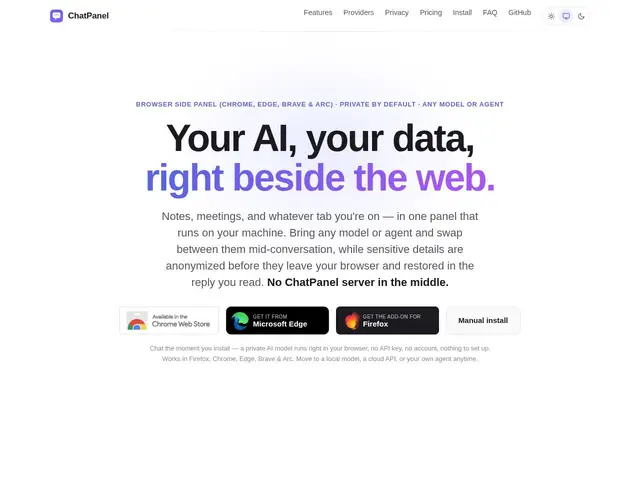
| 5 | Privacy-conscious users wanting model-agnostic AI access from their browser | — | |
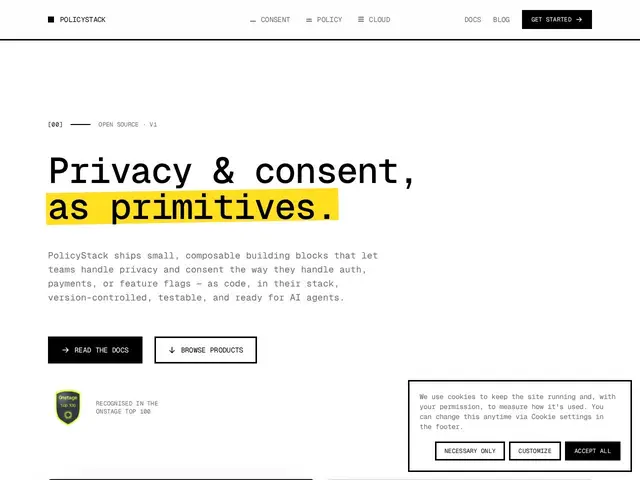
| 6 | Developers wanting privacy/consent management integrated into their codebase | — | |
| 7 | IT/DevOps teams replacing corporate VPNs with Zero Trust access | — | |
| 8 | Businesses needing GDPR-compliant, frictionless bot protection | — | |
| 9 | Organisations d'ingénierie, équipes sécurité/conformité adoptant des agents de code IA | — | |
| 10 | Équipes MCP/API et sécurité déployant des agents IA | — | |
| 11 | Équipes DevOps/SRE et administrateurs système voulant un moniteur d'expiration de certificat sans dépendance pour cron/CI | — | |
| 12 | Équipes construisant des applications LLM soumises à des exigences de conformité (RGPD, AI Act) et de protection des données | — |
macOS app that intercepts and audits MCP server traffic between Claude Desktop or Cursor and connected tools for security oversight.
Free, in-browser generator for robots.txt and llms.txt files that control which AI crawlers can access your site.
Privacy-first browser side panel AI assistant that works with any model or agent and anonymizes sensitive data before it leaves your browser.
Open-source, developer-first privacy and cookie-consent infrastructure with headless consent flows and version-controlled policies.
Open-source WireGuard-based mesh VPN that replaces traditional VPNs with Zero Trust, identity-based device access.
Invisible, privacy-first bot protection using proof-of-work instead of visual puzzles.
Enterprise policy-enforcement layer that watches what coding agents do — prompts, commands, file changes — and blocks or alerts on sensitive data exposure.
Authorization layer that checks every AI agent action against a policy before it runs, with per-action revocation and a full audit trail.
A free Python command-line tool that checks a website's HTTPS certificate and tells you exactly what's wrong with it — expired, untrusted, wrong hostname — instead of a generic connection error.
An open-source trust-boundary gateway that sits in front of OpenAI, Anthropic and Gemini API traffic to redact PII, enforce rate limits, and track usage without touching your app code.