OWASP Zed Attack Proxy (ZAP) web security testing tool.
zaproxy.org
Manually reviewing a large codebase for security vulnerabilities is slow, expensive expert work — and pointing an AI coding assistant at the same task without structure tends to produce shallow, unreliable results. OpenHack sits in between: it packages the way professional security researchers actually work — recon, scoped hypotheses, triage, verification — into a workflow a coding AI can follow step by step, like giving the AI a case file and a procedure instead of just asking it to 'find bugs.' OpenHack is a free, open-source (MIT) research prototype from the Dutch security firm Hadrian, built as a lightweight, file-based workspace that runs inside a coding harness such as Claude Code or Cursor. It keeps all state in plain files — cloned source, recon items, scenario prompts, results, finding candidates, triage decisions — so every step of a review is durable and auditable. It includes 12 OWASP/MITRE-aligned expert agents, a scenario-router for scoped testing, independent finding triage for severity assessment, and human-in-the-loop approval gates before anything is reported as a real finding.
| # | Tool | Best for | Price |
|---|---|---|---|
| 1 | Développeurs | Testeurs de sécurité | — | |
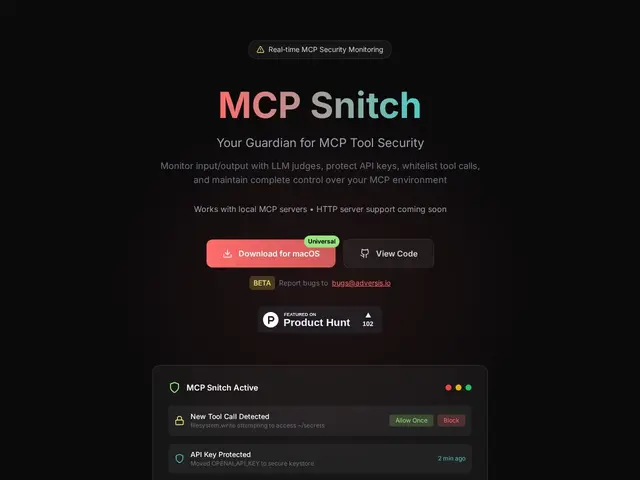
| 2 | Développeurs et équipes utilisant Claude Desktop ou Cursor avec des serveurs MCP tiers, soucieux de la sécurité des appels d'outils IA | — | |
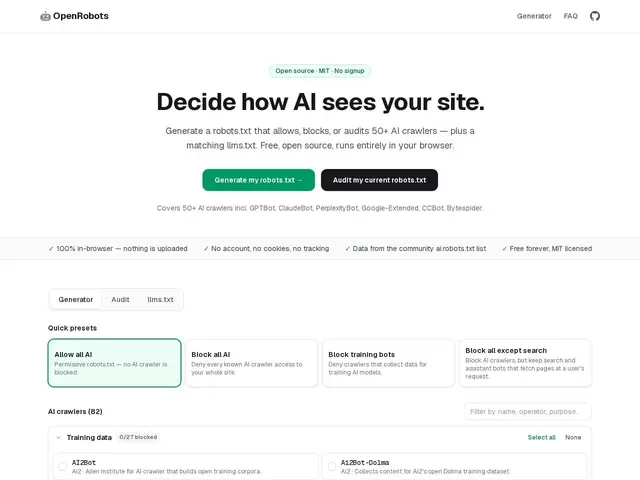
| 3 | Site owners and developers managing AI crawler access | — | |
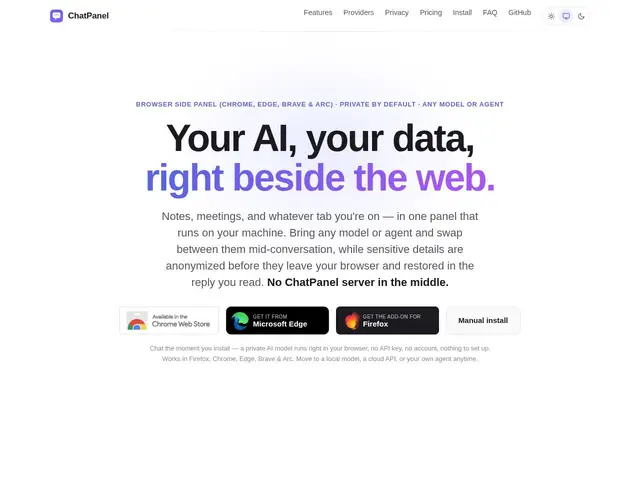
| 4 | Privacy-conscious users wanting model-agnostic AI access from their browser | — | |
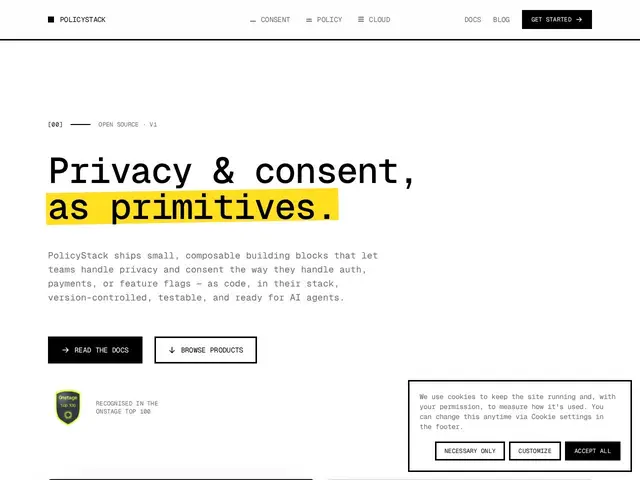
| 5 | Developers wanting privacy/consent management integrated into their codebase | — | |
| 6 | IT/DevOps teams replacing corporate VPNs with Zero Trust access | — | |
| 7 | Businesses needing GDPR-compliant, frictionless bot protection | — | |
| 8 | Organisations d'ingénierie, équipes sécurité/conformité adoptant des agents de code IA | — | |
| 9 | Équipes MCP/API et sécurité déployant des agents IA | — | |
| 10 | Équipes DevOps/SRE et administrateurs système voulant un moniteur d'expiration de certificat sans dépendance pour cron/CI | — | |
| 11 | Équipes construisant des applications LLM soumises à des exigences de conformité (RGPD, AI Act) et de protection des données | — | |
| 12 | Développeurs et petites équipes voulant committer des secrets chiffrés dans Git sans gestionnaire cloud | — |
macOS app that intercepts and audits MCP server traffic between Claude Desktop or Cursor and connected tools for security oversight.
Free, in-browser generator for robots.txt and llms.txt files that control which AI crawlers can access your site.
Privacy-first browser side panel AI assistant that works with any model or agent and anonymizes sensitive data before it leaves your browser.
Open-source, developer-first privacy and cookie-consent infrastructure with headless consent flows and version-controlled policies.
Open-source WireGuard-based mesh VPN that replaces traditional VPNs with Zero Trust, identity-based device access.
Invisible, privacy-first bot protection using proof-of-work instead of visual puzzles.
Enterprise policy-enforcement layer that watches what coding agents do — prompts, commands, file changes — and blocks or alerts on sensitive data exposure.
Authorization layer that checks every AI agent action against a policy before it runs, with per-action revocation and a full audit trail.
A free Python command-line tool that checks a website's HTTPS certificate and tells you exactly what's wrong with it — expired, untrusted, wrong hostname — instead of a generic connection error.
An open-source trust-boundary gateway that sits in front of OpenAI, Anthropic and Gemini API traffic to redact PII, enforce rate limits, and track usage without touching your app code.
A free command-line tool that encrypts your .env secrets file so you can safely commit it to Git, with a pre-commit hook that catches accidental leaks before they happen.