Automated dependency updates
🌐 web
github.com
Dependency vulnerabilities usually surface in a CI pipeline report days after you've already moved on to other work, or worse, get caught by a security team long after code has shipped. CVE Lite CLI brings that check to where you're already working — your terminal, before you push — a bit like a spell-checker for your dependencies that flags problems while you're still writing, not after the document's been sent. CVE Lite CLI is a free, open-source (MIT) tool and an official OWASP Incubator Project, maintained under OWASP governance. It reads your project's lockfile (npm, pnpm, Yarn, Bun), matches packages against the OSV vulnerability database, and distinguishes direct from transitive dependencies so you know exactly which of your own choices introduced a risk versus which came in through something else. It generates copy-and-run fix commands scoped to your package manager, works offline with a cached advisory database, audits override hygiene, flags maintenance risk, and can output an HTML dashboard or SARIF for GitHub Code Scanning, plus a GitHub Action with batched PR fix mode.
| # | Tool | Best for | Price |
|---|---|---|---|
| 1 | Développeurs | — | |
| 2 | Développeurs | — | |
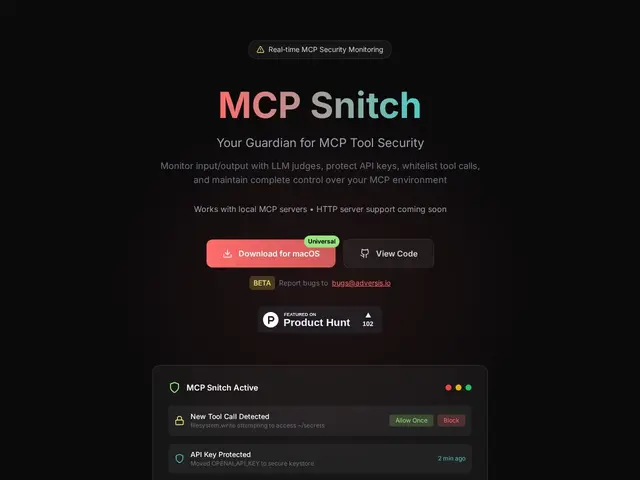
| 3 | Développeurs et équipes utilisant Claude Desktop ou Cursor avec des serveurs MCP tiers, soucieux de la sécurité des appels d'outils IA | — | |
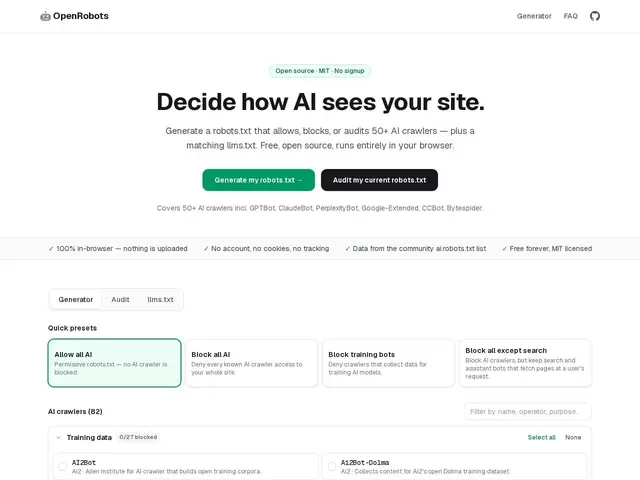
| 4 | Site owners and developers managing AI crawler access | — | |
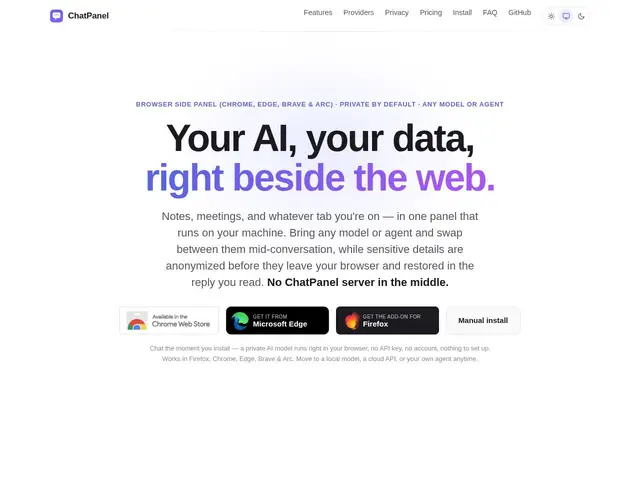
| 5 | Privacy-conscious users wanting model-agnostic AI access from their browser | — | |
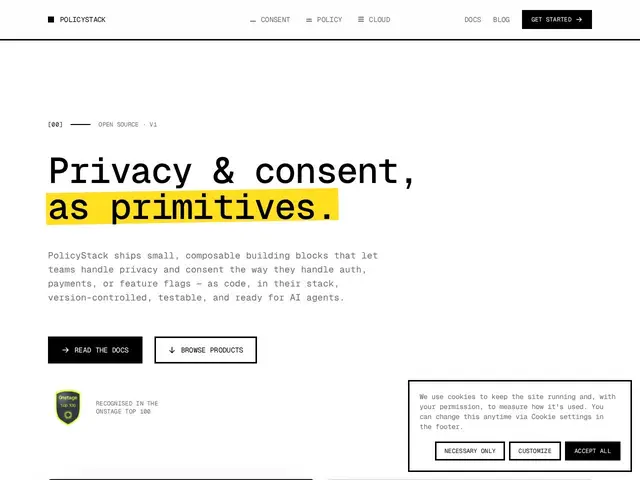
| 6 | Developers wanting privacy/consent management integrated into their codebase | — | |
| 7 | IT/DevOps teams replacing corporate VPNs with Zero Trust access | — | |
| 8 | Businesses needing GDPR-compliant, frictionless bot protection | — | |
| 9 | Organisations d'ingénierie, équipes sécurité/conformité adoptant des agents de code IA | — | |
| 10 | Équipes MCP/API et sécurité déployant des agents IA | — | |
| 11 | Équipes DevOps/SRE et administrateurs système voulant un moniteur d'expiration de certificat sans dépendance pour cron/CI | — | |
| 12 | Équipes construisant des applications LLM soumises à des exigences de conformité (RGPD, AI Act) et de protection des données | — |
macOS app that intercepts and audits MCP server traffic between Claude Desktop or Cursor and connected tools for security oversight.
Free, in-browser generator for robots.txt and llms.txt files that control which AI crawlers can access your site.
Privacy-first browser side panel AI assistant that works with any model or agent and anonymizes sensitive data before it leaves your browser.
Open-source, developer-first privacy and cookie-consent infrastructure with headless consent flows and version-controlled policies.
Open-source WireGuard-based mesh VPN that replaces traditional VPNs with Zero Trust, identity-based device access.
Invisible, privacy-first bot protection using proof-of-work instead of visual puzzles.
Enterprise policy-enforcement layer that watches what coding agents do — prompts, commands, file changes — and blocks or alerts on sensitive data exposure.
Authorization layer that checks every AI agent action against a policy before it runs, with per-action revocation and a full audit trail.
A free Python command-line tool that checks a website's HTTPS certificate and tells you exactly what's wrong with it — expired, untrusted, wrong hostname — instead of a generic connection error.
An open-source trust-boundary gateway that sits in front of OpenAI, Anthropic and Gemini API traffic to redact PII, enforce rate limits, and track usage without touching your app code.