OWASP Zed Attack Proxy (ZAP) web security testing tool.
zaproxy.org
If you've wanted the kind of vulnerability scanning that commercial tools like Burp Suite Pro or Acunetix offer, but without the license fee, BugBounty Arsenal packages a broad set of security checks — over 60 detectors covering injection attacks, misconfigurations, exposed secrets, and known CVEs — into a free, self-hosted, open-source scanner. Every finding is mapped to the OWASP Top 10 with a CVSS score, and rather than leaving you to figure out what to do about it, an "AI Fix Advisor" writes step-by-step remediation guidance for each issue. It goes beyond typical web scanners in two directions: static analysis of Android/iOS mobile apps for hardcoded secrets and weak crypto, and Solidity smart-contract analysis across 28 vulnerability classes for Web3 projects. It also has an unusual gamified mode — a "Red vs Blue Arena" where one side writes offensive detectors and the other defensive ones, scored in real time. Practically, it's built for teams: scheduled/continuous scanning, an attack-surface inventory that tracks new hosts and subdomains weekly, CI/CD integration that can fail a build on new critical findings, and self-hosting via a single Docker Compose command.
| # | Tool | Best for | Price |
|---|---|---|---|
| 1 | Développeurs | Testeurs de sécurité | — | |
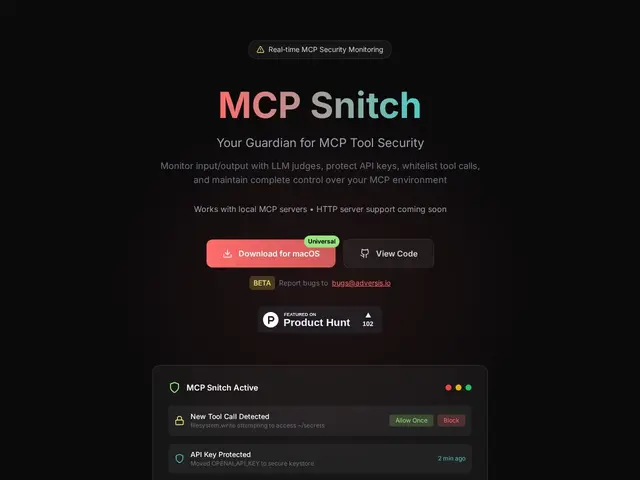
| 2 | Développeurs et équipes utilisant Claude Desktop ou Cursor avec des serveurs MCP tiers, soucieux de la sécurité des appels d'outils IA | — | |
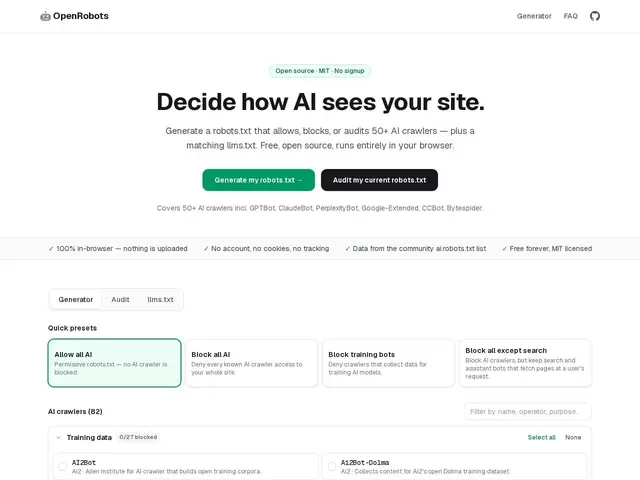
| 3 | Site owners and developers managing AI crawler access | — | |
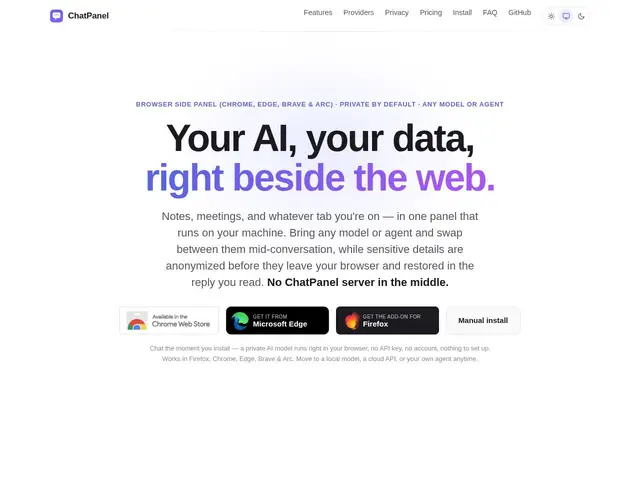
| 4 | Privacy-conscious users wanting model-agnostic AI access from their browser | — | |
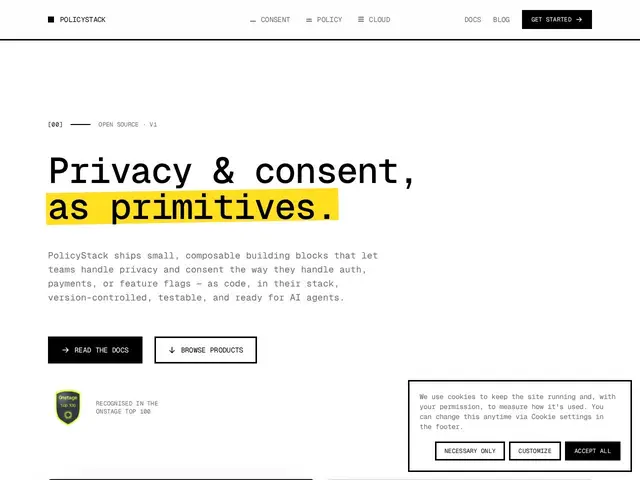
| 5 | Developers wanting privacy/consent management integrated into their codebase | — | |
| 6 | IT/DevOps teams replacing corporate VPNs with Zero Trust access | — | |
| 7 | Businesses needing GDPR-compliant, frictionless bot protection | — | |
| 8 | Organisations d'ingénierie, équipes sécurité/conformité adoptant des agents de code IA | — | |
| 9 | Équipes MCP/API et sécurité déployant des agents IA | — | |
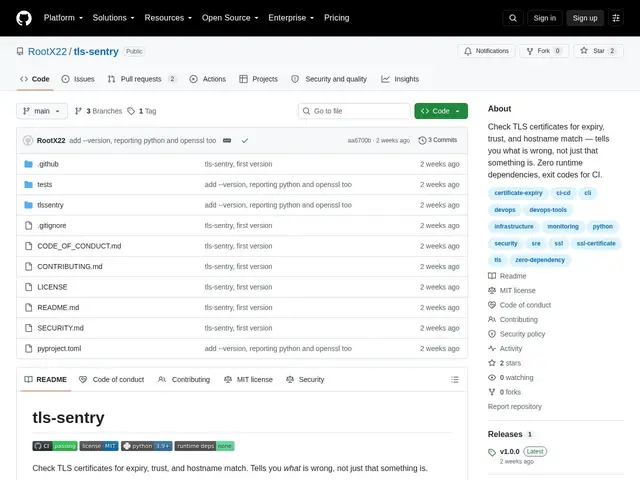
| 10 | Équipes DevOps/SRE et administrateurs système voulant un moniteur d'expiration de certificat sans dépendance pour cron/CI | — | |
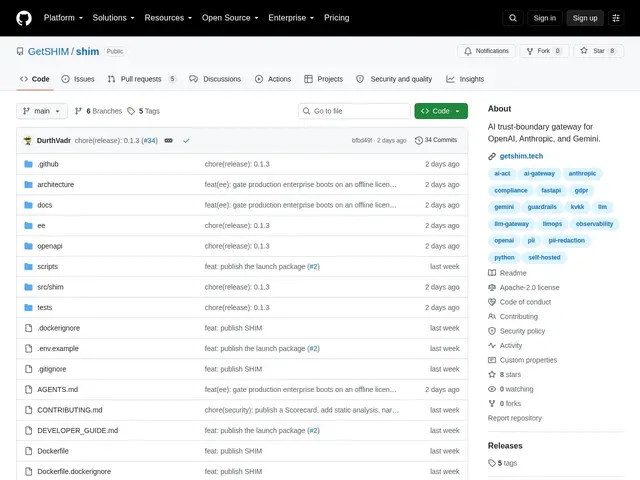
| 11 | Équipes construisant des applications LLM soumises à des exigences de conformité (RGPD, AI Act) et de protection des données | — | |
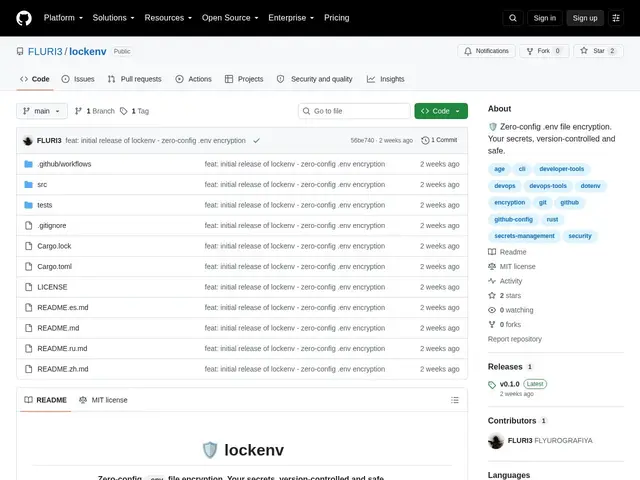
| 12 | Développeurs et petites équipes voulant committer des secrets chiffrés dans Git sans gestionnaire cloud | — |
macOS app that intercepts and audits MCP server traffic between Claude Desktop or Cursor and connected tools for security oversight.
Free, in-browser generator for robots.txt and llms.txt files that control which AI crawlers can access your site.
Privacy-first browser side panel AI assistant that works with any model or agent and anonymizes sensitive data before it leaves your browser.
Open-source, developer-first privacy and cookie-consent infrastructure with headless consent flows and version-controlled policies.
Open-source WireGuard-based mesh VPN that replaces traditional VPNs with Zero Trust, identity-based device access.
Invisible, privacy-first bot protection using proof-of-work instead of visual puzzles.
Enterprise policy-enforcement layer that watches what coding agents do — prompts, commands, file changes — and blocks or alerts on sensitive data exposure.
Authorization layer that checks every AI agent action against a policy before it runs, with per-action revocation and a full audit trail.
A free Python command-line tool that checks a website's HTTPS certificate and tells you exactly what's wrong with it — expired, untrusted, wrong hostname — instead of a generic connection error.
An open-source trust-boundary gateway that sits in front of OpenAI, Anthropic and Gemini API traffic to redact PII, enforce rate limits, and track usage without touching your app code.
A free command-line tool that encrypts your .env secrets file so you can safely commit it to Git, with a pre-commit hook that catches accidental leaks before they happen.