A command-line editor for encrypting secrets inside YAML, JSON, ENV, INI or binary files — using AWS KMS, GCP KMS, Azure Key Vault, age or PGP — so encrypted config can be safely committed to git.
github.com
Almost every team has the same secret-management problem: .env files hold API keys and passwords, so they can never be committed to Git — which means sharing them means Slack messages, shared drives, or a separate secrets tool to set up. lockenv encrypts the file itself with strong, modern cryptography so the encrypted version can live safely in Git right next to the code it belongs to, decrypted only by whoever holds the key. lockenv is an open-source (MIT) Rust CLI using age encryption (X25519 + ChaCha20-Poly1305, ASCII-armored). A single `lockenv init` command generates a key, configures .gitignore, and installs a pre-commit hook that blocks accidental commits of unencrypted secrets. Beyond lock/unlock, it offers a `diff` command that compares two environments without ever printing the actual secret values, plus `audit`, `edit` and `example` commands. It needs no cloud account or SaaS subscription — everything runs offline — and ships as cross-platform binaries (Linux, macOS Intel/Apple Silicon, Windows) or via Cargo. Its README documents an explicit comparison against git-crypt, SOPS and HashiCorp Vault.
| # | Tool | Best for | Price |
|---|---|---|---|
| 1 | Équipes DevOps et SRE gérant des secrets dans des pipelines CI/CD et infrastructures cloud-native | — | |
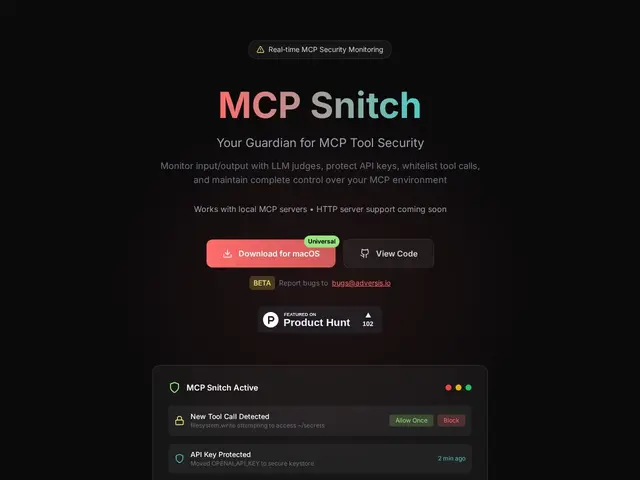
| 2 | Développeurs et équipes utilisant Claude Desktop ou Cursor avec des serveurs MCP tiers, soucieux de la sécurité des appels d'outils IA | — | |
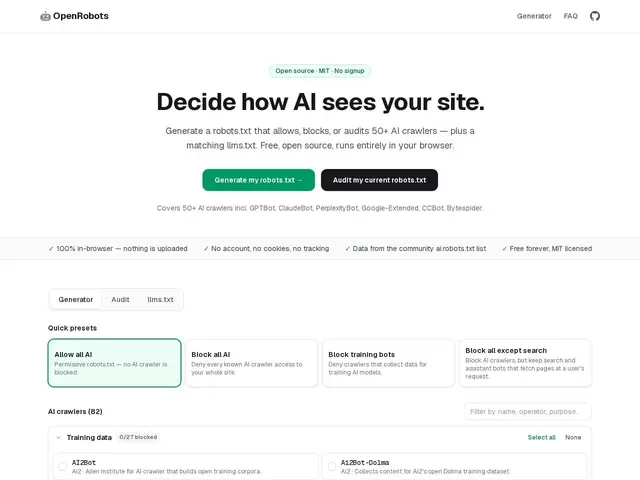
| 3 | Site owners and developers managing AI crawler access | — | |
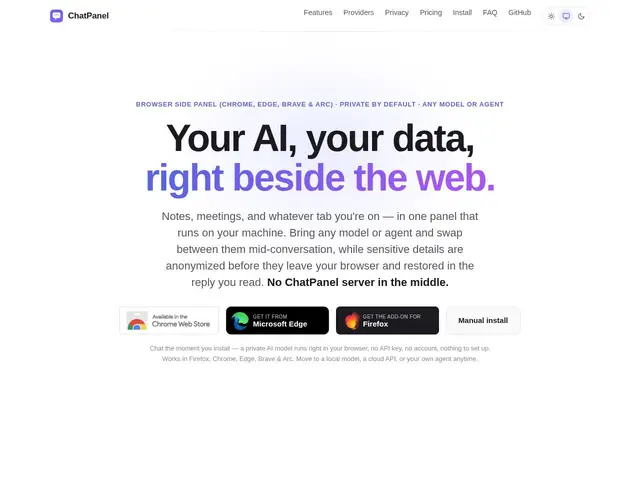
| 4 | Privacy-conscious users wanting model-agnostic AI access from their browser | — | |
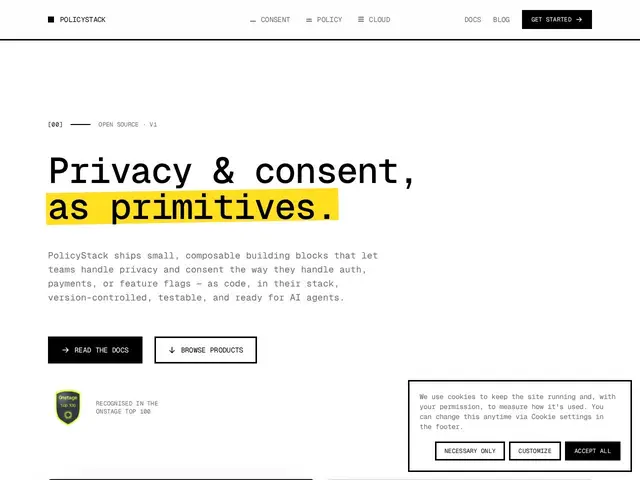
| 5 | Developers wanting privacy/consent management integrated into their codebase | — | |
| 6 | IT/DevOps teams replacing corporate VPNs with Zero Trust access | — | |
| 7 | Businesses needing GDPR-compliant, frictionless bot protection | — | |
| 8 | Organisations d'ingénierie, équipes sécurité/conformité adoptant des agents de code IA | — | |
| 9 | Équipes MCP/API et sécurité déployant des agents IA | — | |
| 10 | Équipes DevOps/SRE et administrateurs système voulant un moniteur d'expiration de certificat sans dépendance pour cron/CI | — | |
| 11 | Équipes construisant des applications LLM soumises à des exigences de conformité (RGPD, AI Act) et de protection des données | — | |
| 12 | Développeurs et équipes sécurité utilisant des agents IA (Claude Code, MCP, LangChain, CrewAI, AutoGen) avec des skills/plugins tiers | — |
A command-line editor for encrypting secrets inside YAML, JSON, ENV, INI or binary files — using AWS KMS, GCP KMS, Azure Key Vault, age or PGP — so encrypted config can be safely committed to git.
macOS app that intercepts and audits MCP server traffic between Claude Desktop or Cursor and connected tools for security oversight.
Free, in-browser generator for robots.txt and llms.txt files that control which AI crawlers can access your site.
Privacy-first browser side panel AI assistant that works with any model or agent and anonymizes sensitive data before it leaves your browser.
Open-source, developer-first privacy and cookie-consent infrastructure with headless consent flows and version-controlled policies.
Open-source WireGuard-based mesh VPN that replaces traditional VPNs with Zero Trust, identity-based device access.
Invisible, privacy-first bot protection using proof-of-work instead of visual puzzles.
Enterprise policy-enforcement layer that watches what coding agents do — prompts, commands, file changes — and blocks or alerts on sensitive data exposure.
Authorization layer that checks every AI agent action against a policy before it runs, with per-action revocation and a full audit trail.
A free Python command-line tool that checks a website's HTTPS certificate and tells you exactly what's wrong with it — expired, untrusted, wrong hostname — instead of a generic connection error.
An open-source trust-boundary gateway that sits in front of OpenAI, Anthropic and Gemini API traffic to redact PII, enforce rate limits, and track usage without touching your app code.
A security scanner that formally verifies AI agent "skills" (tools/plugins) across 22 frameworks for supply-chain risks before you trust them.