License Detector
A CLI that reads the actual license text of your dependencies — not just declared metadata — across 21+ package ecosystems including npm, pip, Maven, Go, and Cargo, entirely offline.
🔗 Visit License Detector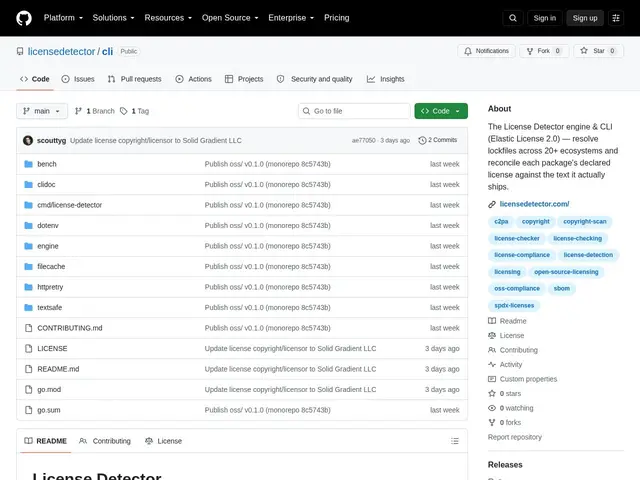
Description
A package's declared license in package.json or setup.py isn't always the real story — licenses get modified, dual-licensed, or misdeclared, and metadata-only scanners miss all of that. License Detector actually reads the license text itself to figure out what's really there.
License Detector resolves lockfiles across 21+ package ecosystems (npm, pip, Maven, Go modules, Cargo, Ruby, .NET, and more), works fully offline using an embedded license corpus, and flags modified licenses, dual/OR licensing, and other gaps that metadata-only tools miss. It outputs in text, JSON, CSV, or SBOM (SPDX/CycloneDX) formats, supports SARIF for CI integration, lets you define custom compliance policies, and can gate a build via exit codes. It also does deeper asset scanning for media rights and AI-generation provenance (C2PA credentials). The CLI itself is free and open source under the Elastic License 2.0; a hosted GitHub App at licensedetector.com adds PR checks and a dashboard as a separate, proprietary offering.
💬 Our review
The short version: License Detector's core differentiator — actually reading license text instead of trusting declared metadata — is a legitimate advantage over most open-source license scanners, and the free CLI alone is enough for most individual developers or small teams.
FOSSA and Black Duck are the established enterprise-grade options, with mature dashboards, legal-team workflows, and broad ecosystem coverage, but they're commercial products with enterprise pricing to match. ScanCode Toolkit is the closest free/open-source peer in spirit — it also does deep license-text analysis rather than metadata lookup — so the two are worth comparing directly if you want a fully offline, free option; License Detector's edge is its explicit 21+ ecosystem lockfile resolution and CI-ready SARIF/exit-code gating out of the box. If your team needs dashboards and PR-level checks without setting up your own CI wiring, the hosted GitHub App is the natural upsell, but the CLI alone covers real compliance-scanning needs for free.
💰 Pricing
📊 Global score
🤖 AI-enriched data
CLI gratuite et open source (Elastic License 2.0) ; app GitHub hébergée payante (licensedetector.com) pour dashboard et checks PR
Pros
Analyse le texte réel des licences, pas seulement les métadonnées déclarées
21+ écosystèmes de paquets supportés (npm, pip, Maven, Go, Cargo...)
Fonctionne entièrement hors ligne
Formats de sortie multiples (JSON, CSV, SBOM, SARIF) pour intégration CI
Cons
Dashboard et checks PR réservés à l'offre payante hébergée
Moins de maturité que FOSSA ou Black Duck en entreprise
Tarification de l'app hébergée non précisée