Vigolium
A free, open-source vulnerability scanner that combines fast, deterministic security checks with an optional AI agent that plans and triages findings on its own — built for penetration testers and security teams who want automation without losing precisio
🔗 Visit Vigolium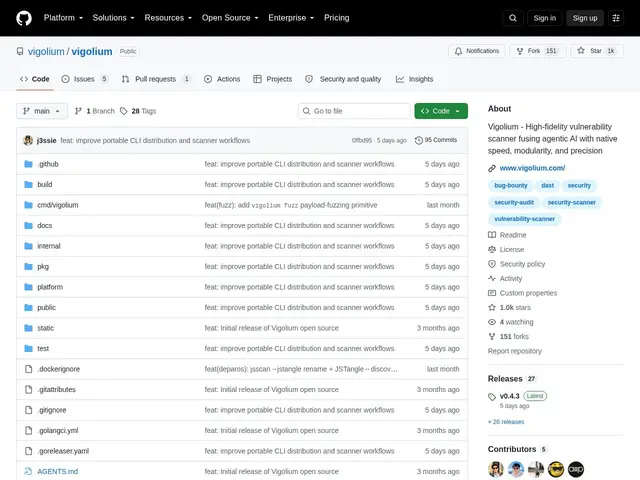
Description
Traditional vulnerability scanners are fast and predictable but can miss context-dependent bugs, while newer AI-driven tools can reason about complex logic flaws but are often slow and unpredictable. Vigolium tries to get both: a deterministic scanning engine for speed and coverage, plus an optional AI agent you can hand control to when a target needs deeper, more creative investigation — like having both a checklist and a detective on the same case.
Vigolium is a free, open-source (AGPLv3) vulnerability scanner with 323 scanner modules (207 active, 116 passive) covering the OWASP Top 10, deployable as a CLI or in server mode with a REST API and web dashboard. Its 'Native Scan' mode runs a fast, deterministic multi-phase pipeline (content discovery, spidering, active/passive auditing), while 'Agentic Scan' hands control to an LLM-driven harness that selects modules, writes custom JavaScript extensions on the fly, and triages findings. It supports out-of-band testing (OAST), multi-session authenticated scanning for IDOR/BOLA bugs, and can ingest OpenAPI specs, Postman collections, Burp Suite exports, or cURL commands as scan input. A paid Vigolium Cloud Console exists for teams that want a hosted alternative.
💬 Our review
The short version: if you run security assessments and want both fast deterministic coverage and an AI agent that can dig into complex logic flaws when needed, Vigolium is a free, actively developed tool built around that exact combination.
Compared to established open-source scanners like OWASP ZAP or Nikto, which are purely deterministic, Vigolium's Agentic Scan mode is the real differentiator — an LLM-driven harness that can write custom test extensions and reason through multi-step authenticated flows (IDOR/BOLA) that rule-based scanners routinely miss. Against closed-source AI-native scanners, Vigolium's open-source AGPLv3 core keeps the detection logic auditable and self-hostable, with a paid Cloud Console only as an optional convenience layer, not a requirement.
The honest limits: it's a young project (around 1,000 GitHub stars), so its module coverage and community-contributed detections are still smaller than a decade-old tool like ZAP, and Agentic Scan mode consumes LLM API credits (bring-your-own-key), adding a variable cost on top of the free scanner. AGPLv3 also brings source-disclosure obligations for a modified network service, the same caveat as other AGPL security tools. For a pentester or security team that wants deterministic scanning with an AI escalation option when logic bugs are suspected, it's a strong free pick; for the widest possible community rule coverage on a shoestring budget, an established tool like ZAP still has the deeper library.
💰 Pricing
📊 Global score
🤖 AI-enriched data
Open source (licence AGPLv3), gratuit et auto-hébergeable. Le mode Agentic Scan consomme des crédits API LLM (BYOK). Console Cloud payante disponible en option.
Pros
323 modules de scan (207 actifs, 116 passifs) couvrant l'OWASP Top 10
Mode Agentic Scan piloté par IA — peut écrire des extensions custom et détecter des failles logiques (IDOR/BOLA)
Testing out-of-band (OAST) et scan multi-session authentifié
Ingestion directe d'OpenAPI, Postman, Burp Suite ou cURL comme point de départ
Cons
Projet jeune (~1000 étoiles GitHub), couverture communautaire encore limitée vs ZAP
Mode Agentic Scan consomme des crédits API LLM en plus (BYOK)
Licence AGPLv3 — obligations de divulgation de code pour usage réseau modifié