BlacksmithAI
A hacking-simulation tool that uses a team of AI agents — each specialized like a real penetration-testing crew member — to automatically probe a system for security weaknesses, from initial scanning all the way to proving an exploit works.
🔗 Visit BlacksmithAI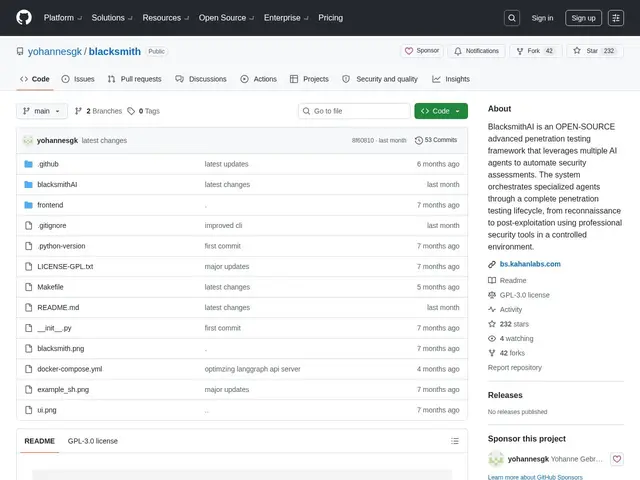
Description
Professional penetration testing usually means hiring a human security team to manually work through a checklist: scan for open doors, find weaknesses, try to break in, and report what they found. BlacksmithAI automates that entire process by splitting the job across multiple specialized AI agents — one that maps out the target, one that hunts for vulnerabilities, one that attempts exploitation, and one that reports on what could happen next — all running real, industry-standard security tools inside a controlled Docker container.
BlacksmithAI is a free, open-source (GPL-3.0-licensed, with commercial licensing available) framework that orchestrates its agent pipeline — reconnaissance, scanning/enumeration, vulnerability analysis, exploitation, and post-exploitation — through the "mini-kali" Docker image, which bundles professional pentesting tools. It supports a wide range of LLM providers and offers both a web UI and a terminal/CLI interface, aimed at professional penetration testers, security researchers and DevSecOps teams who want to automate parts of a testing engagement rather than running every tool by hand.
💬 Our review
The short version: if you already run manual pentests and want to automate the repetitive reconnaissance-through-exploitation grind, BlacksmithAI is a genuinely useful open-source starting point — but it's a tool for people who already understand pentesting, not a replacement for that expertise.
It sits in a fast-growing niche alongside projects like Pentest-Swarm-AI, all racing to prove that multi-agent LLM orchestration can meaningfully speed up offensive security work. Being free and open source under GPL-3.0 (with a commercial license path if you need one) makes it easy to evaluate with zero cost commitment, unlike commercial AI pentesting platforms that gate everything behind a sales call. The honest caveat: this class of tool is early — expect to supervise its output carefully rather than trust exploitation results blindly, and only ever run it against systems you're explicitly authorized to test.
💰 Pricing
📊 Global score
🤖 AI-enriched data
GPL-3.0, gratuit. Licences commerciales disponibles séparément, tarifs non communiqués.
Pros
Gratuit et open source (GPL-3.0)
Pipeline multi-agents complet (recon → exploitation → post-exploitation)
Outils professionnels intégrés via Docker (mini-kali)
Interface web ET ligne de commande
Cons
Nécessite déjà des compétences en pentesting pour être utilisé correctement
Catégorie encore jeune, résultats à superviser attentivement
Pas de service managé, self-hosted uniquement