DataGrail
Software that automates the paperwork of privacy law — like GDPR requests to delete someone's data — across every tool your company uses, instead of your legal team chasing each app by hand.
🔗 Visit DataGrail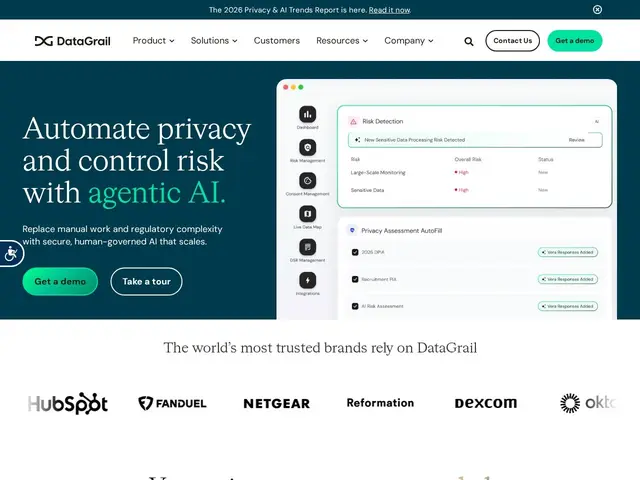
Description
When someone asks a company to delete their personal data under GDPR or CCPA, answering that request properly means checking every tool the company uses — the CRM, the email platform, the analytics dashboard — and most of that is done by hand with spreadsheets and emails to IT. DataGrail automates that entire chase: it maps where personal data actually lives across a company's software, and automatically fulfills privacy requests across thousands of connected apps.
DataGrail is an agentic data privacy platform built around a live, AI-powered data map, automated consent/cookie management, and a request manager that fulfills Data Subject Requests across 2,500+ connected apps. It also generates Privacy Impact Assessments automatically and maintains a risk register with recommended remediation steps, guided by an AI agent called Vera. It positions itself against OneTrust, emphasizing simpler risk management and a much larger pre-built integration catalog (1,500+ SaaS integrations versus the 50-200 typical of competitors).
💬 Our review
The short version: DataGrail replaces the spreadsheet-and-email scramble of privacy compliance with automated data mapping and request fulfillment across thousands of tools at once.
The headline differentiator — 1,500+ pre-built SaaS integrations against a typical 50-200 for rivals — is a real practical advantage if your company's software stack is sprawling and non-standard, since integration coverage is usually the actual bottleneck in privacy tooling, not the workflow logic itself. Being positioned explicitly as a OneTrust alternative signals it's chasing the incumbent's customers with a simpler, presumably faster-to-deploy product. The honest caveat: pricing is entirely quote-based with nothing public, so there's no way to compare cost against OneTrust or smaller tools like Osano without going through a sales process, and for a smaller company with a handful of SaaS tools and light compliance obligations, this is likely enterprise-grade overkill priced accordingly. If your organization juggles many regulations (GDPR, CCPA, Colorado, Virginia) across a large, messy app stack, the integration breadth alone justifies evaluating it; if your privacy surface is small, get a quote before assuming you need this much machinery.
💰 Pricing
📊 Global score
🤖 AI-enriched data
Pricing not public — quote-based, positioned as enterprise-grade compliance tooling
Pros
1,500+ pre-built SaaS integrations vs. 50-200 typical of rivals
Automates Data Subject Request fulfillment across thousands of apps
Live AI-powered data map instead of manual spreadsheets
Automated Privacy Impact Assessment generation
Cons
No public pricing — requires a sales quote to compare
Likely overkill and priced for enterprise, not small teams
Positioned as OneTrust alternative — same category of complexity