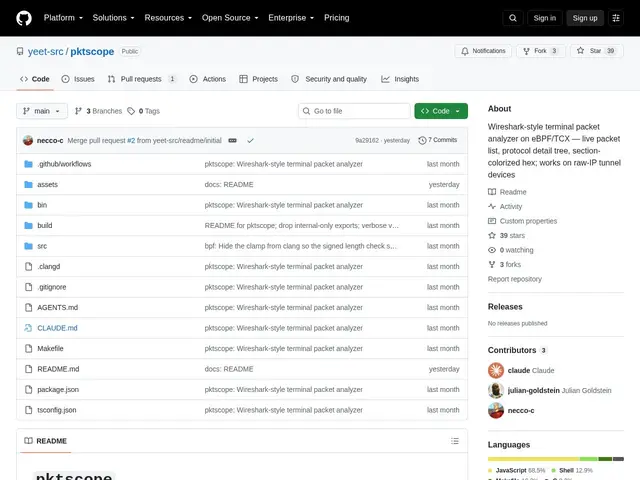
A Wireshark-style network packet analyzer that runs entirely in the terminal, built on eBPF for handling tricky raw-IP tunnel traffic like WireGuard and GRE.
github.com
3 tools found
A Wireshark-style network packet analyzer that runs entirely in the terminal, built on eBPF for handling tricky raw-IP tunnel traffic like WireGuard and GRE.
A terminal UI for tshark, inspired by Wireshark.
The world’s foremost and widely-used network protocol analyzer. [![Open-Source Software][OSS Icon]](https://github.com/wireshark/wireshark) ![Freeware][Freeware Icon]

